
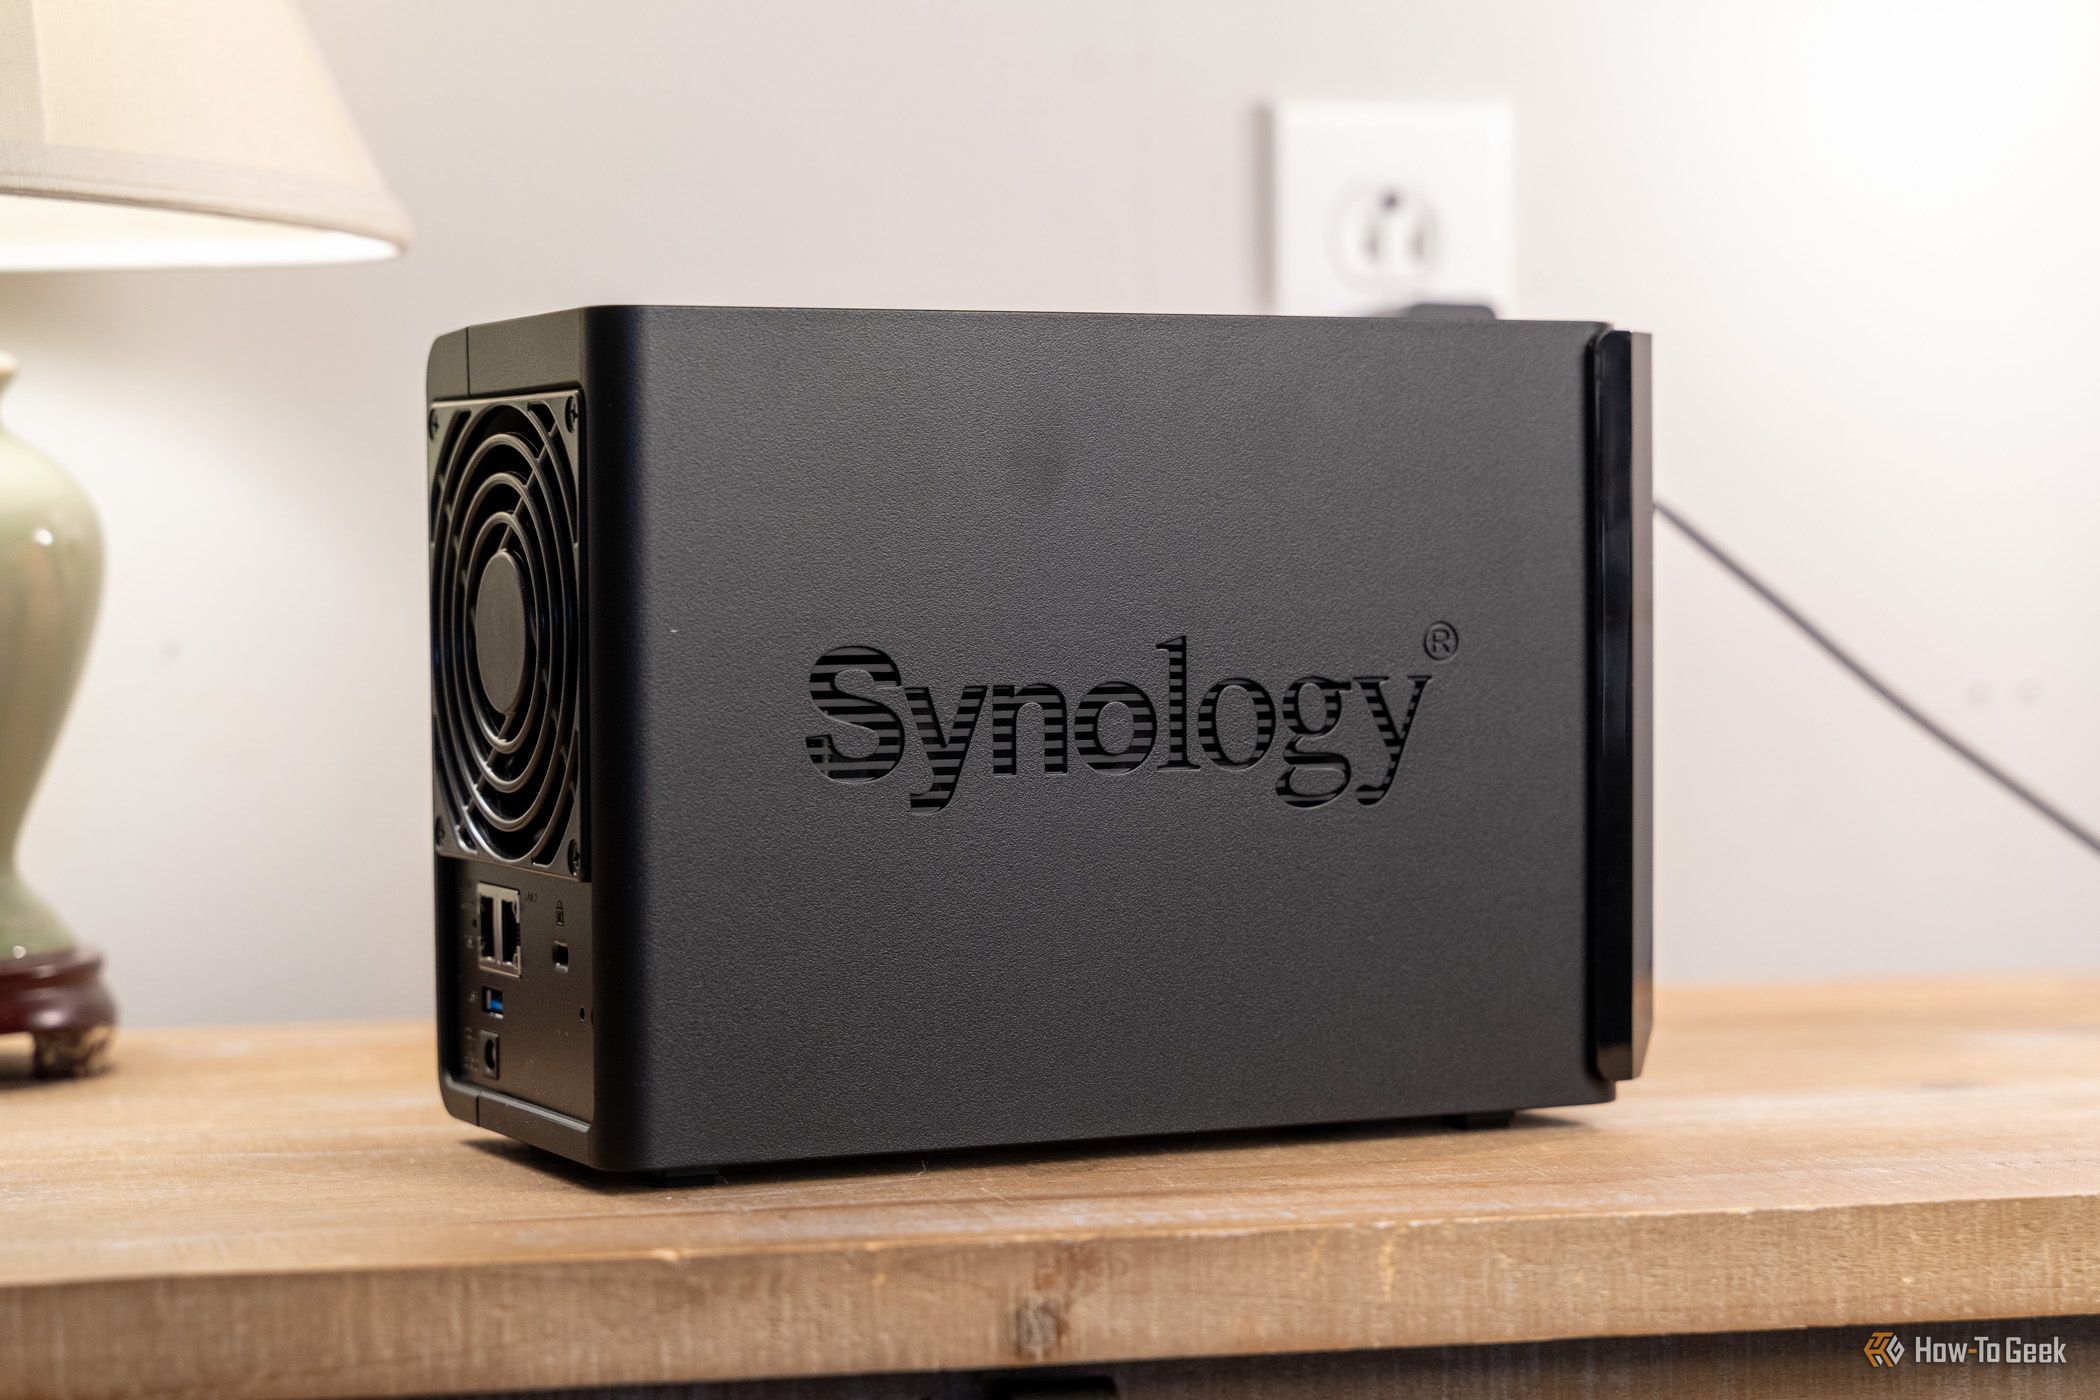
Synology has been scrambling to fix the PHP2Shell vulnerabilities since the PHP developers released emergency security patches on October 21, and the company confirmed that a number of its NAS packages were affected. Now the story has taken a twist, as Synology reports that attackers are exploiting the flaws, and the US cybersecurity agency CISA has added them to its Known Exploited Vulnerabilities catalog. Synology is now extending security fixes to older DiskStation Manager (DSM) versions, following the discovery of a separate ransomware campaign targeting outdated NAS systems.


